Latest posts
Cyber security awareness month: How about a card game?
Every year we do the little extra dance to spread cyber security awareness around us, and every year this is usually centered around phishing or passwords - which is fair; it's what we encounter the most. But - how about trying something like a game about security?
Break-the-glass: Can you?
Establishing break-the-glass accounts is a well-established practice and recommendation. But do you make sure it actually is usable if the worst would happen?
PIM without the pilgrimage
This is one of those minor frustrations that are actually quite annoying: You have access to several tenants and need to activate PIM roles. This means a pilgrimage through the Azure portal and switching between tenants and performing the activations. But it doesn't have to be like this.
Protecting against Device Code phishing
Device code phishing is on the rise and normal measures don't seem to help - not even phishing resistant MFA. Why is that? How does this technique even work? What can actually be done?
How apps can become first-class citizens in Microsoft Sentinel
Many applications that are developed either as an in-house application or a SaaS offering often provide functionality that are useful or even essential for Security Operations Center to have insight into. So, how can we offer a direct integration into security solutions?
Application-level monitoring and SOC
There is a fundamental difference between application-level and OS-level monitoring. The latter is easier as there is a common understanding how they work. However, applications have their own personalities - how does a SOC even begin to handle them?
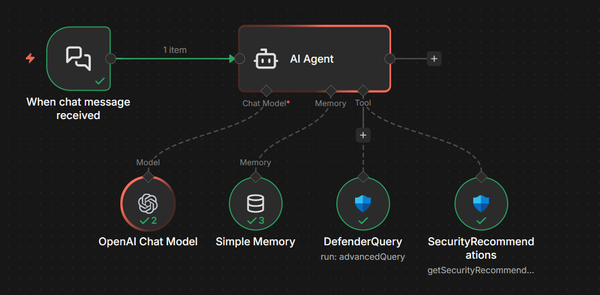
I made a n8n node for Microsoft Defender
While testing n8n for use with Microsoft Defender, I found that there was no integrations available for the Microsoft Defender API - so I made my own. Let me show you how it works.
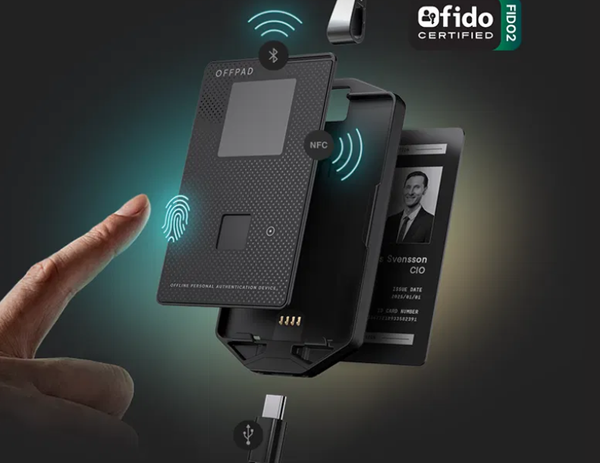
OFFPAD+ - A review
A simple review of the OFFPAD+ device which has helped me ditch the QR-code fatigue and just make phishing-resistant MFA easier and more intuitive to use daily.
Vulnerability deep-dive with KQL
In some cases, Microsoft Defender will report vulnerable software in your organization but the device(s) are patched - so why is it reporting as vulnerable? Certain software gets
Detection rules as code
With the introduction of the msgraph-provider, it is now quite easy to deploy your custom detection rules to Microsoft Defender fully automatically using Terraform. The immediate benefit
Entra ID role definitions - an introduction
Microsoft's Entra ID has a ever-growing list of built-in role definitions and you can even create your own. But how do they actually work?

Entra ID Conditional Access: Sign-in Frequency gotcha
The general idea of Sign-in Frequency condition in the Entra ID Conditional Access seems very appealing: When you have a scenario where a user wants to activate